 OpenSourceMalware.com - Community Threat Intelligence (opens in new tab)
Security professionals sharing intelligence on malicious packages, repositories, and CDNs to protect the open source ecosystem.
Added by Adrian Sanabria
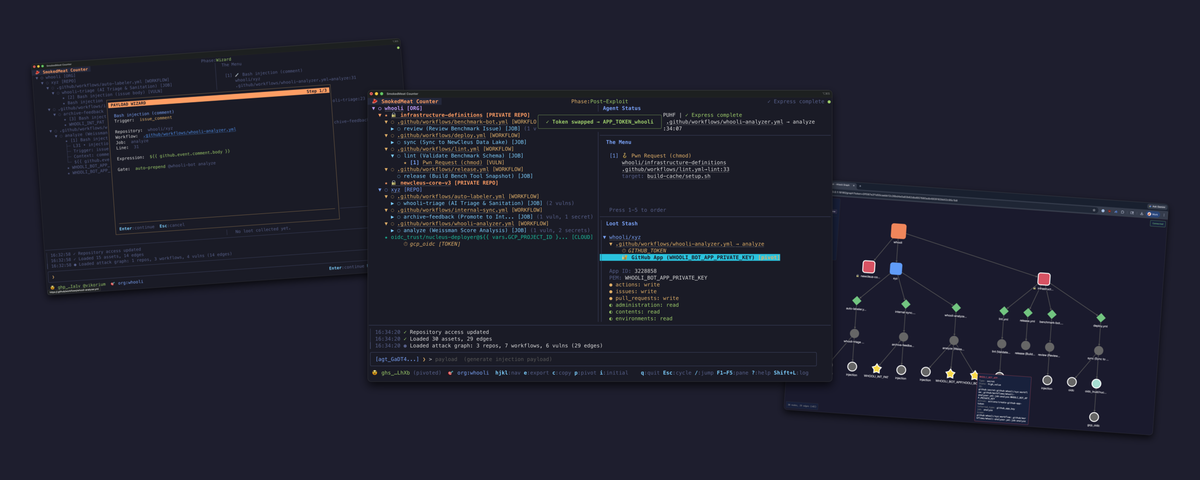
In March 2026, TeamPCP unleashed mayhem on the software supply chain: compromising Trivy, LiteLLM, KICS, Telnyx, and dozens of npm packages, proving that CI/CD pipelines are the softest target. Today we
Added by Adrian Sanabria